Documents
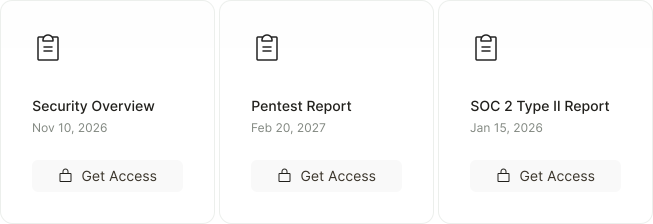
Share SOC 2, ISO, pentest, and other reports in a structured, access-controlled library.

Give prospects one clear place to request access, sign the right NDA, and download watermarked documents while your team keeps control.
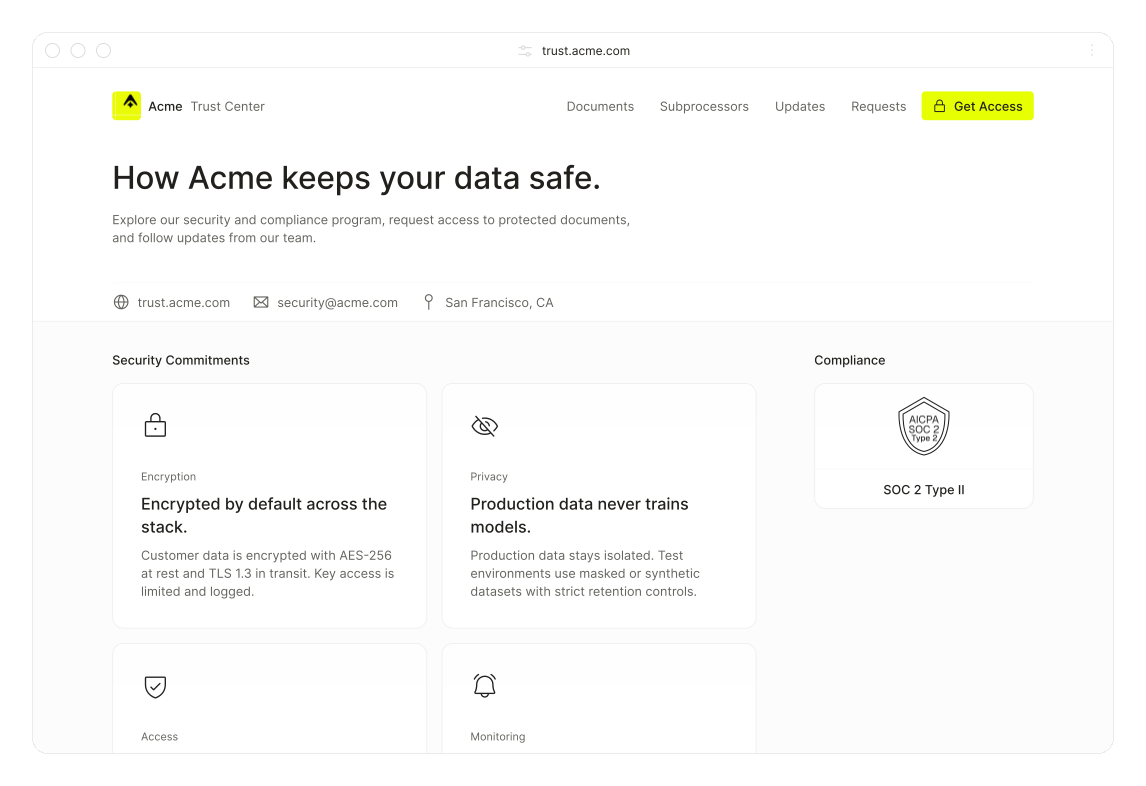
Help buyers find the right materials faster, while your team decides what is public, restricted, or approval-only.
Share key security materials from one Compliance Portal, and decide what stays public, restricted, or approval-only.
Review access requests in Slack and keep rules aligned with the way your team already works.
Let prospects sign an NDA in the Compliance Portal before downloading protected, watermarked files.
Let prospects sign in with SSO or magic links without creating another account.
Choose which policy, subprocessor, report, or audit updates subscribers should receive.
Approve requests in Slack, support SSO or magic links, and keep every permission attached to the right company.
Organize policies, controls, reports, audits, and vendors into clear categories instead of scattered compliance materials.
Share SOC 2, ISO, pentest, and other reports in a structured, access-controlled library.
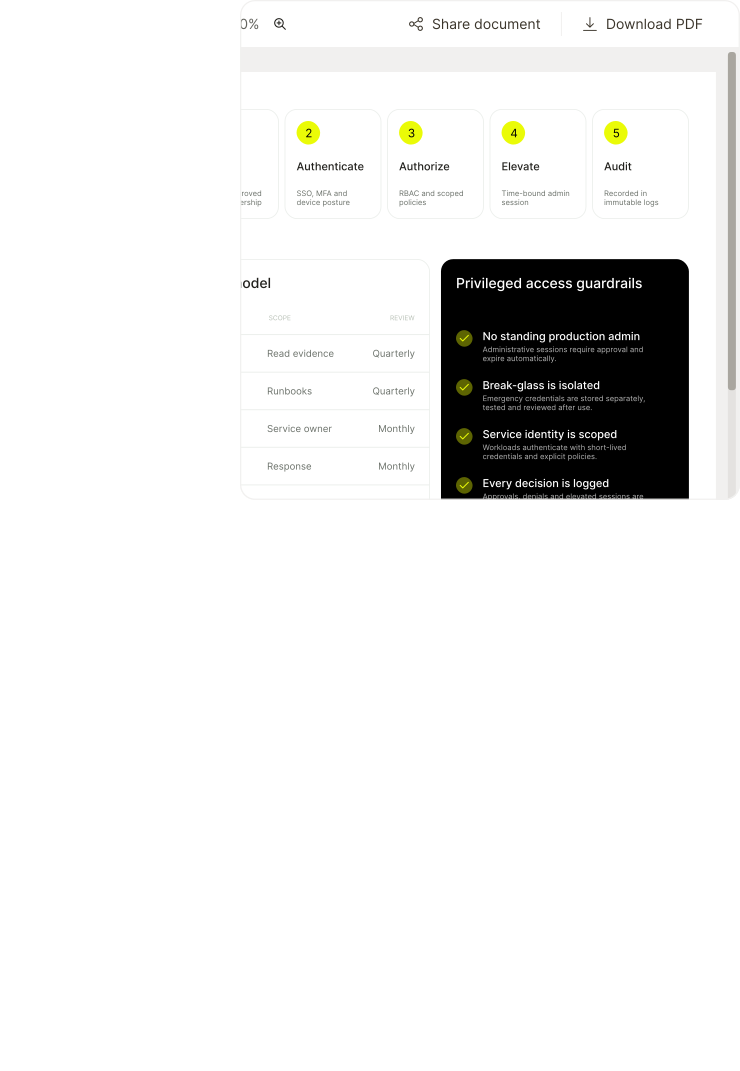
Let buyers open, review, and download each PDF in a secure, focused experience.
Give buyers the audit history and historical compliance materials they need when appropriate.
List subprocessors with the context buyers need to assess risk.
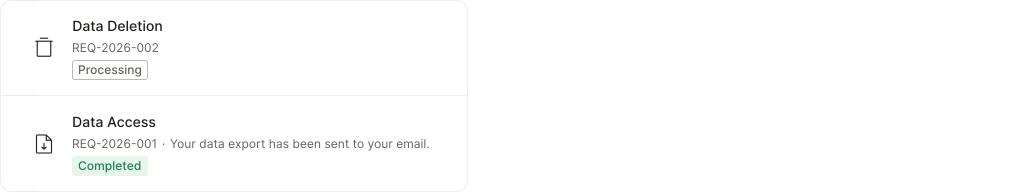
Handle customer data requests through a guided flow, from identity check to export delivery.
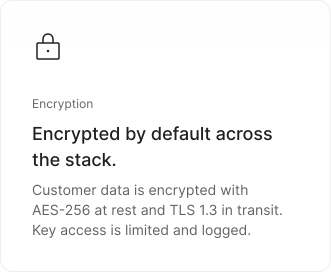
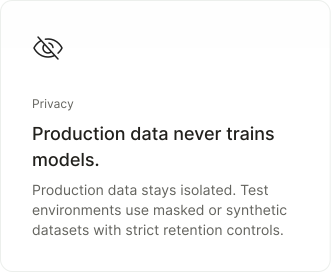
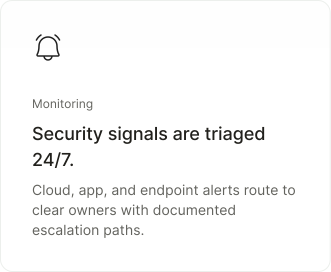
Explain what your company commits to in security, in a concise, scannable, and engaging format.
Security teams use ZebraByte to share the right materials, protect sensitive documents, and keep access requests moving.
“ZebraByte handled our SOC 2 and compliance, so we could focus on building.”
Reference teams and compliance-ready workflows



Can’t find the framework you are looking for?
Talk to us — we may be able to include it in the program.
Not seeing the framework you are looking for?
Reach out — we may already support it in the programme.