



Context
Organization, stakeholders, needs, limits and scope of the ISMS.

ZebraByte helps prepare for ISO/IEC 27001 through risk management, controls, policies, evidence and ongoing processes.
Management system
The standard defines requirements for an Information Security Management System based on risk.The scope, risk assessment, risk treatment, controls and evidence must reflect the actual organization.
This makes the difference between an operable ISMS and a set of documents prepared only for certification.
Clauses 4–10
Annex A is only a part of the standard. Clauses 4–10 describe how the system is defined, operated, operated, verified and improved.
Organization, stakeholders, needs, limits and scope of the ISMS.
Policy, responsibilities and management involvement in the program.
Risks, opportunities, objectives and risk management methodology.
Resources, skills, awareness, communication and documented information.
Implementation of the treatment plan and operation of the chosen controls.
Monitoring, measurement, internal audit and management review.
Inconsistencies, corrective actions and continuous improvement.
Annex A
Not all controls apply automatically to each organization. Risk assessment and risk treatment determine what is relevant, and Statement of Applicability documents the decision.
Policy, roles, supplier relationships, threat intelligence, incident management and other governance controls.
Screening, terms of employment, awareness, responsibilities and processes that reduce human risk.
Secure areas, equipment, working environments and physical protection of information and infrastructure.
Identity, access control, logging, vulnerability management, cryptography, networks and secure development.
Risk loop
Controls are not selected in isolation. They must be traceable back to the risks, decisions and objectives of the organization.
Systems, information, processes, suppliers and dependencies within the scope.
Threats, vulnerabilities, impact, probability and their own assessment criteria.
Reduce, avoid, transfer or accept risk through a documented decision.
Read relevant risk controls and document the applicability in the Statement of Applicability.
Reviews, approvals, logs and results showing that the measures are operating in practice.
Risk, scope and controls are updated as the business or infrastructure changes.
Technical evidence
Where scope requires technical measures, security engineering must be able to demonstrate what is actually happening in the infrastructure.
Vezi Cyber SecurityCertification journey
ZebraByte prepares and can help with the operation of the program. Evaluation and certification remain independent.
Scope, risk assessment, controls, policies, evidence and remediation before the independent assessment.
Internal audit, management review, findings and corrective actions before the external auditor evaluates the system.
The certification body shall verify the preparation of the ISMS and the basis required for the detailed assessment.
Evaluators verify that the ISMS and the selected controls are deployed and operated within the declared scope.
Risk reviews, internal audits, management reviews and continuous improvement do not stop after certification.
Responsibility
Readiness, ISMS design, risk management, controls, evidence, remediation and continuous operation within the agreed scope.
It holds the decisions, risk, responsibilities and effective operation of the information security management system.
It independently assesses the ISMS and, when the requirements are met, issues the certification.ZebraByte is not a certification body.
External assurance
The certificate and assurance materials can be distributed through the Trust Center within the scope of the certificate. The internal workspace, risk register and other sensitive information remain separate.
Vezi Trust Center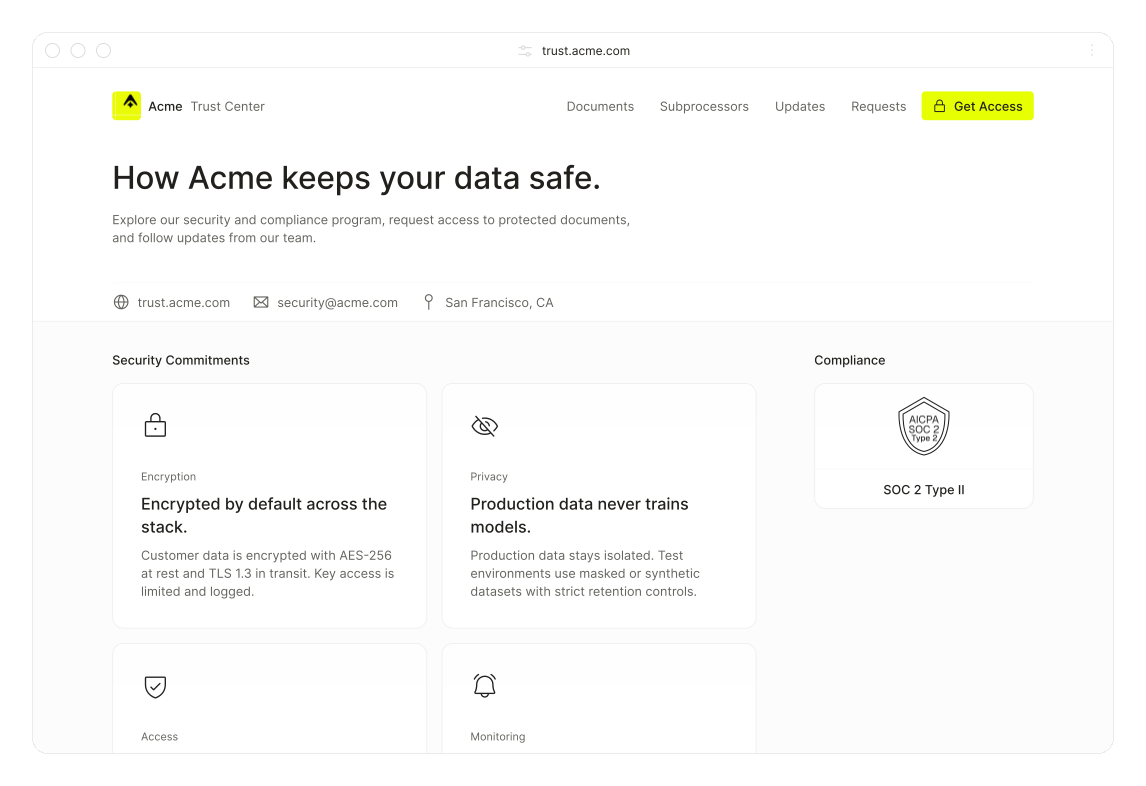
Practical examples from the platform library about compliance and security programs built for growing organizations.
See all case studies.

No.ZebraByte can help with readiness, ISMS design, risk management, controls, evidence and remediation. Certification is issued by an independent certification body after scope and system evaluation.
The organization evaluates its risks and obligations, selects relevant controls and documents inclusion or exclusion in the Statement of Applicability.
It is the document linking risk management to the relevant controls in Annex A and explaining their applicability. We treat it as a living part of the program, not as a table prepared solely for audit.
No. Policies and documents are required, but certification is based on a management system operated in practice. Access reviews, supplier management, incident handling and other processes must be supported by real evidence.
ISMS continues: risk reviews, internal audits, management reviews, corrective actions and updating of controls. Certification does not turn the program into a static artefact.
We can start with readiness and turn the result into a continuously followed program in the ZebraByte platform.
Talk about ISO27001
Can’t find the framework you are looking for?
Talk to us — we may be able to include it in the program.
Not seeing the framework you are looking for?
Reach out — we may already support it in the programme.