





How Ahrefs became ISO 27001 certified in 3 months
Reference case study. This material documents a real ISO 27001 journey and is kept as an example of how an expert-supported compliance platform can formalize an established engineering organization. Ahrefs is not represented as a ZebraByte customer.
The Challenge: Ahrefs needed formal assurance for enterprise customers without replacing its engineering culture with a separate compliance bureaucracy.
The Approach: Existing infrastructure and security practices were converted into a practical ISMS, material gaps were prioritized, evidence was organized centrally and specialists carried much of the compliance coordination.
The Results:
- audit-ready in weeks rather than a conventional multi-month preparation cycle;
- approximately 80% less audit-readiness time in the reference engagement;
- substantially lower external-consulting overhead than a traditional high-touch engagement;
- minimal disruption to engineering and infrastructure teams.
About Ahrefs
Ahrefs is a Singapore-based SEO and marketing technology company founded in 2010. Its platform is used by marketers, agencies and enterprises to analyze backlinks, keywords, competitors and search performance.
The company operates a large amount of its infrastructure in-house to support continuous web crawling and very large datasets. That operating model creates a mature technical environment, but enterprise buyers still need standardized evidence that security governance is documented, repeatable and independently assessable.
The challenge
Ahrefs did not need a certification to discover that security mattered. The driver was different: as enterprise activity increased, prospects began requesting ISO 27001 and SOC 2 assurance.
The project therefore had to satisfy several goals at once:
- strengthen customer trust through recognized assurance;
- preserve the company’s existing engineering culture;
- make the ISMS reflect real infrastructure rather than a generic template;
- minimize manual work for engineers and security staff;
- reach audit readiness quickly enough to support active commercial opportunities.
The difficult part of ISO 27001 is rarely writing a long list of controls. It is deciding what is sufficient for the organization’s actual risks, documenting how controls operate and proving that the system is maintained over time.
Why the traditional approach created friction
A conventional route can involve hiring dedicated internal compliance staff or relying heavily on external consultants. Both can be expensive for a technical company when context has to be transferred repeatedly.
The reference experience highlighted a common problem: teams may understand individual ISO 27001 controls yet still be uncertain about scope, evidence quality and what “sufficient” implementation looks like in practice.
That uncertainty leads to over-implementation. Teams can start treating every control as an isolated project and assume everything must be perfected before speaking with an auditor.
A better model is iterative: identify the actual gaps, establish a working management system, prepare evidence and keep improving it over time.
Turning existing practices into an ISMS
The successful approach in this reference case had three major parts.
1. Design around existing operations
Instead of imposing unrelated processes, the compliance program documented how security and infrastructure already worked. Those practices became the foundation of the Information Security Management System.
This matters because a policy that describes a fictional process is difficult to operate and difficult to audit. A policy that accurately describes a mature existing practice is easier to own, test and improve.
2. Centralize evidence and coordination
Risk mapping, policy work, control evidence, vendor information and audit preparation were managed as one program. Subject-matter experts still provided technical evidence, but they were not responsible for orchestrating every compliance task themselves.
3. Prioritize meaningful gaps
The goal was not theoretical perfection. The program focused on differences between documented expectations and real operations, then closed the gaps that materially affected security and audit readiness.
This is the model ZebraByte supports through its cloud platform: the organization can operate the system itself, a professional adviser can manage it for clients, or ZebraByte Managed Compliance can take on more of the operational work.
Results
Rapid readiness
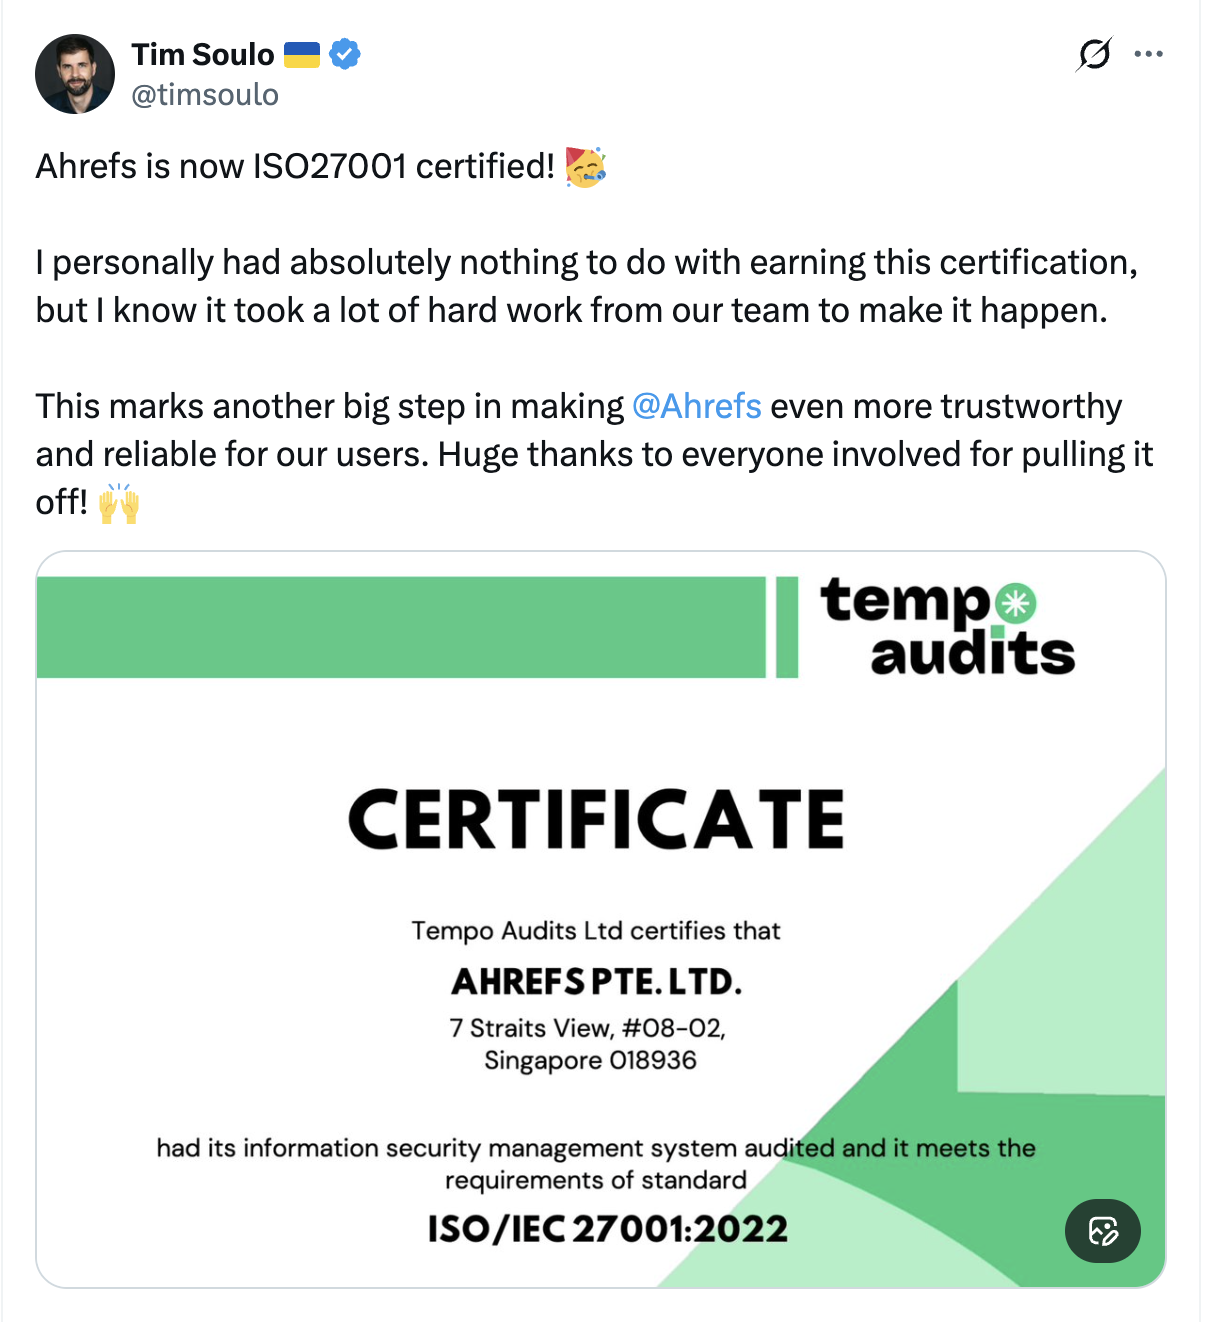
The reference project moved from structured compliance work to audit readiness in roughly ten weeks and reached ISO 27001 certification at around thirteen weeks.
The important point is not that every organization will follow the same timeline. Scope, maturity, auditor availability and remediation work all affect duration. The transferable lesson is that an organization with strong existing security practices can move much faster when those practices are mapped and evidenced efficiently.
Conserving internal resources
A platform plus specialist-support model can remove much of the work that normally lands on engineering:
- mapping controls;
- organizing evidence;
- maintaining policy workflows;
- tracking risks and remediation;
- assessing third parties;
- coordinating audit preparation.
Engineering still owns the technical reality. It simply does not have to own the administrative machinery around proving it.
Financial impact
The reference engagement reported a 70–80% reduction in consultant fees compared with a traditional large-consultancy-style approach, alongside low internal overhead.
That kind of saving depends heavily on scope and organization size, so it should be treated as a case-specific outcome rather than a universal ZebraByte promise. It does demonstrate why combining software, structured workflows and targeted expert time can be economically different from a consulting-only model.
Why it worked
Ahrefs already had strong security and engineering discipline. The compliance program succeeded by formalizing what worked, automating repeatable work and focusing specialist effort on the places where judgement was required.
Once the ISO 27001 foundation existed, related assurance work such as SOC 2, privacy and AI governance could reuse parts of the same risk, control and evidence model.
What another organization can learn from this case
A mature technical team approaching ISO 27001 should ask:
- Which security processes already operate reliably but lack formal evidence?
- Which controls genuinely require remediation rather than more documentation?
- Can evidence be collected continuously from existing systems?
- Are policies aligned with actual operations?
- Is specialist time being spent on judgement or on repetitive administration?
- Can the resulting control library support other frameworks later?
The central lesson is that compliance should translate strong engineering into trustworthy evidence, not replace strong engineering with paperwork.
