



Data records
We inventory the relevant data categories, their sensitivity and the business context in which they are used.

Data, processing activities, DPIA, transfers, suppliers, rights requests and evidence — organized in the same program with risks, controls and technical security measures.
Privacy graph
RoPA, DPIA, vendor reviews and security do not have to live in documents unrelated to each other. In ZebraByte processing activities, risks, vendors, controls and evidence can be tracked as elements of the same cloud program.
The platform helps in the organization and traceability. It does not determine which law is applicable and does not replace legal interpretation when it is necessary.
Privacy lifecycle
The program starts from actual data and activities andins the link between risk, process and evidence.
We inventory the relevant data categories, their sensitivity and the business context in which they are used.
We document the purposes, categories of data subjects and data, recipients, transfers, retention and measures relevant to processing activities.
DPIA, TIA and other assessments are related to processing, vendors, risks and measures that address the risk.
Requests such as access, rectification or deletion are followed as owners processes, deadlines and verifiable actions.
We update records, policies, third parties and evidence when processes, data or infrastructure changes.
RoPA / processing record
Evidence of processing activities becomes useful when itins sufficient context for review and is updated when the process changes.
Why there is processing and what outcome the organization seeks.
Categories of data subjects and categories of data involved.
Who receives or may access the data, including relevant third parties.
Transfer to third countries or international organizations, where applicable.
The periods or criteria for retention and deletion, where they may be established.
A general description of the relevant technical and organizational measures.
Impact assessments
DPIA and TIA do not have to be separate files. We link them to processing, transfers, suppliers, risks and measures that justify the decision.
Data Protection Impact Assessment
For processing that may pose a high risk to the rights and freedoms of individuals, we structure the risk assessment, mitigation measures and decisions that must be documented.
Transfer Impact Assessment
For relevant international transfers, we keep the context of the transfer, parties involved, guarantees and additional measures in a processing and supplier-related assessment.
Data subject requests
Data subjects’ requests can be tracked through a controlled process with owner, tasks and status, without scattering the information between emails, documents and separate lists.
Access should be limited to persons who need to process the application, and unnecessary personal data should not be entered in open fields only for convenience.
View the Privacy Management documentation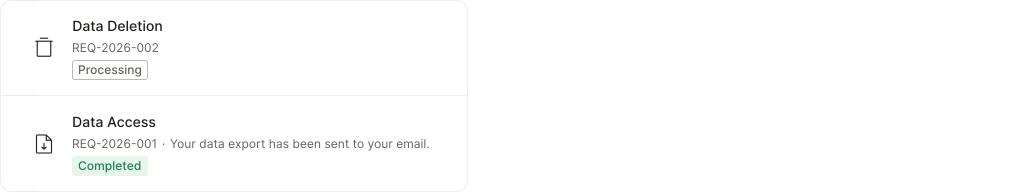
Processor chain
Vendors, processors, subprocessors and transfers must be tracked along with processing activities and the risks they pose.
Inventory, roles, services, DPAs and the context in which providers process or may access personal data.
We link the relevant documents and guarantees to the supplier and the processing activities it supports.
We identify relevant transfers and keep assessments and associated documentation where necessary.
Changes to suppliers, services or processing conditions are returned to the privacy program and risk review.
Technical measures
The risk to personal data cannot be dealt with only through policies and notices. Technical and organizational measures must be related to the risks and processing activities for which they exist.
Vezi Cyber SecurityLegal reference
GDPR is Regulation (EU) 2016/679.ZebraByte assists in the organization and operation of the privacy program and related technical measures; the service does not replace legal advice when a specific legal interpretation is required.
Regulamentul (UE) 2016/679 — EUR-LexZebraByte helps with the structure and operation of the privacy program, evidence and technical measures. When a specific legal interpretation is required, it must be validated with the relevant legal specialist or DPO.
Evidence of processing activities is useful when it reflects actual processes, recipients, transfers, retention and security measures and is updated when processing changes.
GDPR requires a DPIA prior to any processing that may generate a high risk to the rights and freedoms of individuals. The specific assessment depends on the nature, context, purpose and risks of the processing.
Yes. Rights requests can be tracked through a workflow with owners and tasks. Access should be limited to people who need to process the application and avoid unnecessary entering personal data into free fields.
Yes, when measures and risks overlap.The same technical control or evidence can support multiple obligations, without assuming that the frameworks are legally equivalent.
We can start with a gap assessment and turn the result into a continuously tracked program in the ZebraByte platform.
Talk about ZBTKEEP
Can’t find the framework you are looking for?
Talk to us — we may be able to include it in the program.
Not seeing the framework you are looking for?
Reach out — we may already support it in the programme.