



Security
Basic criterion for each report SOC2
Access control, change management, monitoring, incident response and other controls that protect systems from unauthorized access.

We define scope, organize controls and evidence, pursue remediation and prepare the organization for independent auditor engagement.
Type I
Type II
Assurance program
SOC2 is an assurance framework for service organizations. The report provides customers and reviewers with an independent assessment of the controls in scope.
Useful readiness builds a program that can be demonstrated in the audit and operated after the audit — not documents that exist only for the engagement period.
Trust Services Criteria
Security is the basic criterion. The others are added when the product, commitments or customer requirements justify their inclusion in scope.
Basic criterion for each report SOC2
Access control, change management, monitoring, incident response and other controls that protect systems from unauthorized access.
When availability is part of commitments
Capacity, backup, recovery, continuity and service monitoring when the organization makes availability commitments.
For complete, valid and timely processing
Controls supporting the accuracy, authorization and integrity of the processes relevant to the assessed service.
For designated confidential information
Classification, access, protection and controlled removal of information that the organization has undertaken to treat as confidential.
When privacy comes into play
Processes for collection, use, retention, disclosure and other relevant obligations regarding personal information.
Report type
Two types of report, two different assurance objectives.
Evidence lifecycle
The program is built around the real environment, risks and controls that the organization can operate and demonstrate.
We define the services, systems, locations, suppliers and trust services relevant criteria for engagement.
→We link risks to existing controls and identify gaps that need to be addressed before the audit.
→Owners, policies, access reviews, vulnerability management, change management and all other activities are part of an operable program.
→We collect, review and approve evidence next to the controls they support, without a separate sprint before the audit.
→We organize the materials, check the remaining gaps and prepare the owners for the auditor’s questions and samples.
→After the report, controls, evidence and remediation continues.SOC2 does not end on the report issue date.
↻Control evidence
ASOC2 control does not become real just because it exists in a policy. When the scope requires technical measures, we link them to the activities and evidence that exists in the infrastructure.
Vezi Cyber SecurityEngagement roles
Readiness, control mapping, evidence structure, remediation tracking and continuous operation of the program within the agreed scope.
It holds the processes, real controls, business decisions and information that only internal owners can confirm or operate.
It performs the certification engagement and issues the report.ZebraByte does not present itself as a CPA firm and does not issue the SOC2 report.
Trust distribution
The SOC2 report and other trust documents can be distributed controlled through the Trust Center, with approved access and protected documents.
Vezi Trust Center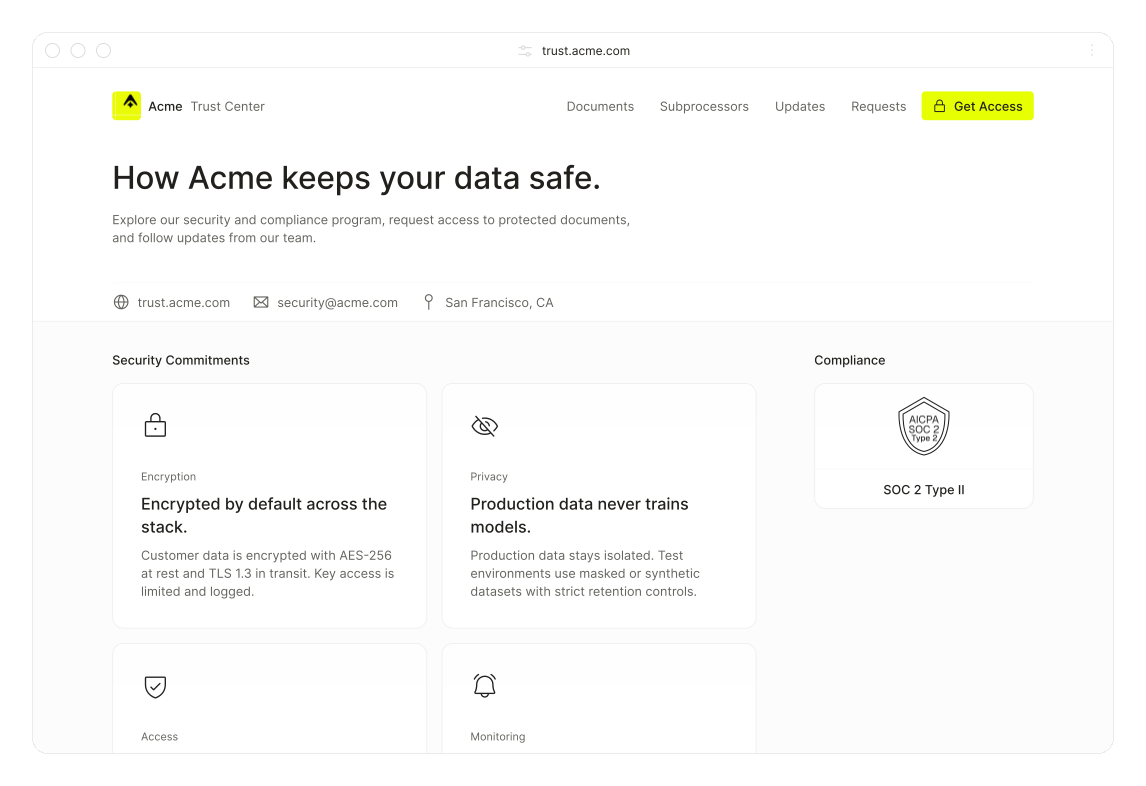
Practical examples from the platform library about compliance and security programs built for growing organizations.
See all case studies.

No.SOC2 is a certification engagement resulting in a report issued by a qualified independent auditor.ZebraByte helps with the readiness and operation of the program, does not issue the report.
Type I evaluates the design of the controls at a given time. Type II evaluates the design and operation of the controls over a defined period. The choice depends on the business objective, the maturity of the program and the requirements of the customer or auditor.
Security is the core criterion for each report, and the other criteria are selected according to service, commitments and the organization’s context.
Yes, the same measures, risks and evidence can support more obligations when requirements overlap, instead of duplicating the work just because the framework has a different name.
The program continues: checks need to be operated, evidence need to be updated, findings need to be corrected, and the report and trust documents can be distributed controlled through the Trust Center where appropriate.
We can start with readiness and continue with controls, evidence, remediation and program operation after the report is issued.
Talk about SOC2
Can’t find the framework you are looking for?
Talk to us — we may be able to include it in the program.
Not seeing the framework you are looking for?
Reach out — we may already support it in the programme.