




March 22, 2026
Console
Access Logs
Get full visibility into every action in your organization with SIEM-ready audit logs auditors expect during SOC 2 and ISO 27001 reviews.
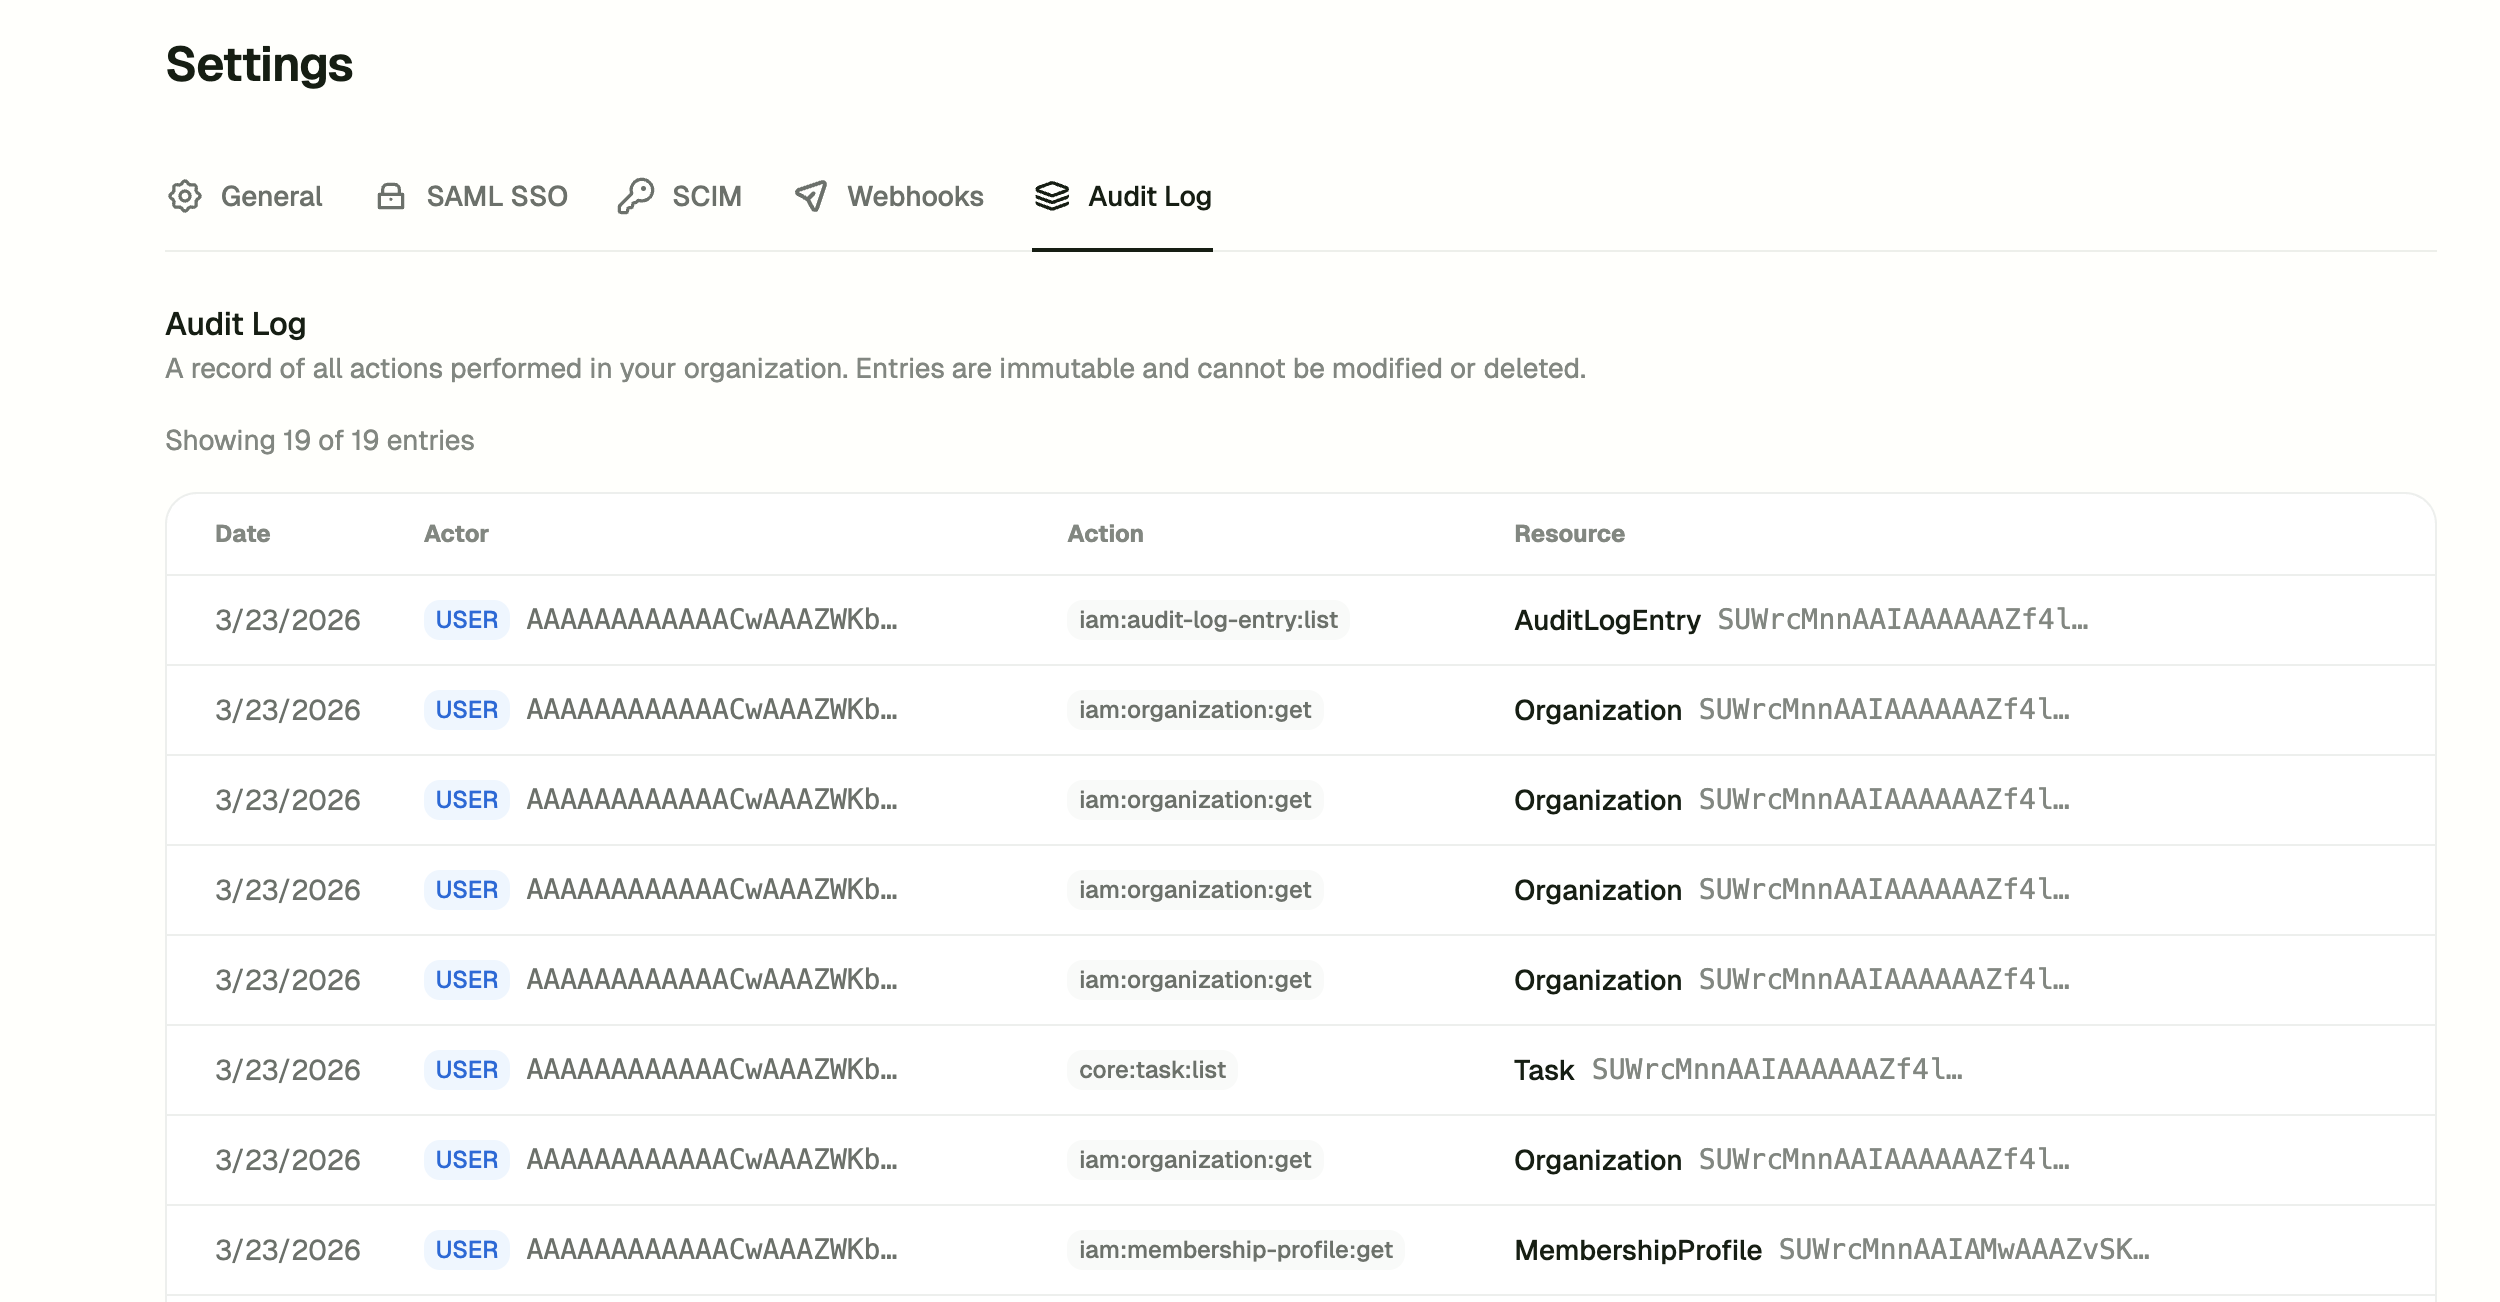
Every action in your organization is now logged and visible in one place. Who signed in, who updated a policy, who invited a new team member, when it happened, and from where.
This is the kind of observability auditors love to see. During a SOC 2 or ISO 27001 review, one of the first questions is “can you show me an audit trail?” Now you can, without exporting anything or stitching together data from different sources.
The logs are SIEM-ready, so if your security team already uses a centralized logging platform, they can pull ZebraByte events right into their existing dashboards and alerting workflows.
