




June 19, 2026
IAM
Personal API Tokens
Create, list, and revoke your own bearer tokens for scripting against the ZebraByte API, without sharing a service account with your team.
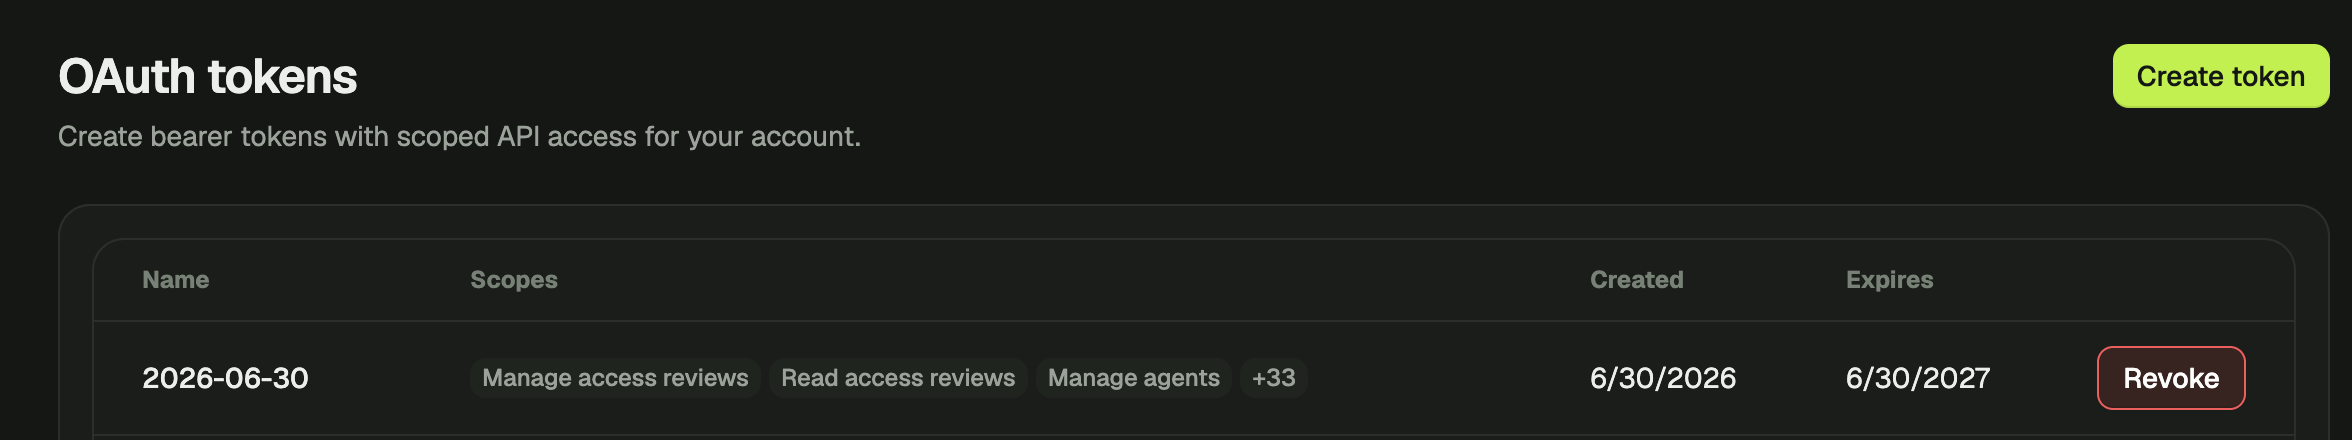
Until now, calling the ZebraByte API outside the console meant either building an OAuth2 app or borrowing a token meant for something else.
Personal API tokens fix that. Head to /me/oauth-tokens in the console, and you can create a bearer token scoped to your own identity, list the tokens you’ve issued, and revoke any of them on the spot. Every v1 API scope is now registered and enforced, so tokens only work for what they were actually granted.
Auditors get the v1:iam:read scope by default, which covers the read-only API access most audit tooling needs without a separate request.
