




Scaleway
Connect Scaleway as an access review source using an IAM secret key and Organization ID to review who has IAMReadOnly access to your account.
the platform reads your Scaleway Organization’s IAM users through the Scaleway IAM API so you can review who has access.
Prerequisites
Section titled “Prerequisites”- the platform organization administrator access
- A Scaleway API key whose bearer holds the
IAMReadOnly(orIAMUserReadOnly) permission, so it can list the Organization’s users. The account Owner has this by default - Your Scaleway Organization ID, from the console under Organization Settings (use Copy ID next to the Organization name)
Collected Fields
Section titled “Collected Fields”| the platform field | Scaleway field | Notes |
|---|---|---|
| Name | first_name and last_name | Falls back to the username, then the email |
email | ||
| Role | type | owner → Owner, member → Member |
| Admin | type | Flagged as an administrator when type is owner |
| Status | status and locked | Inactive when the account is locked or its invitation is still pending |
| MFA | two_factor_enabled | Whether two-factor authentication is enabled (falls back to the mfa flag) |
| Last login | last_login_at | When the user last signed in |
| External ID | id | Stable identifier used to track the account across reviews |
| Created at | created_at | When the user was added to the Organization |
Step 1: Create an API Key
Section titled “Step 1: Create an API Key”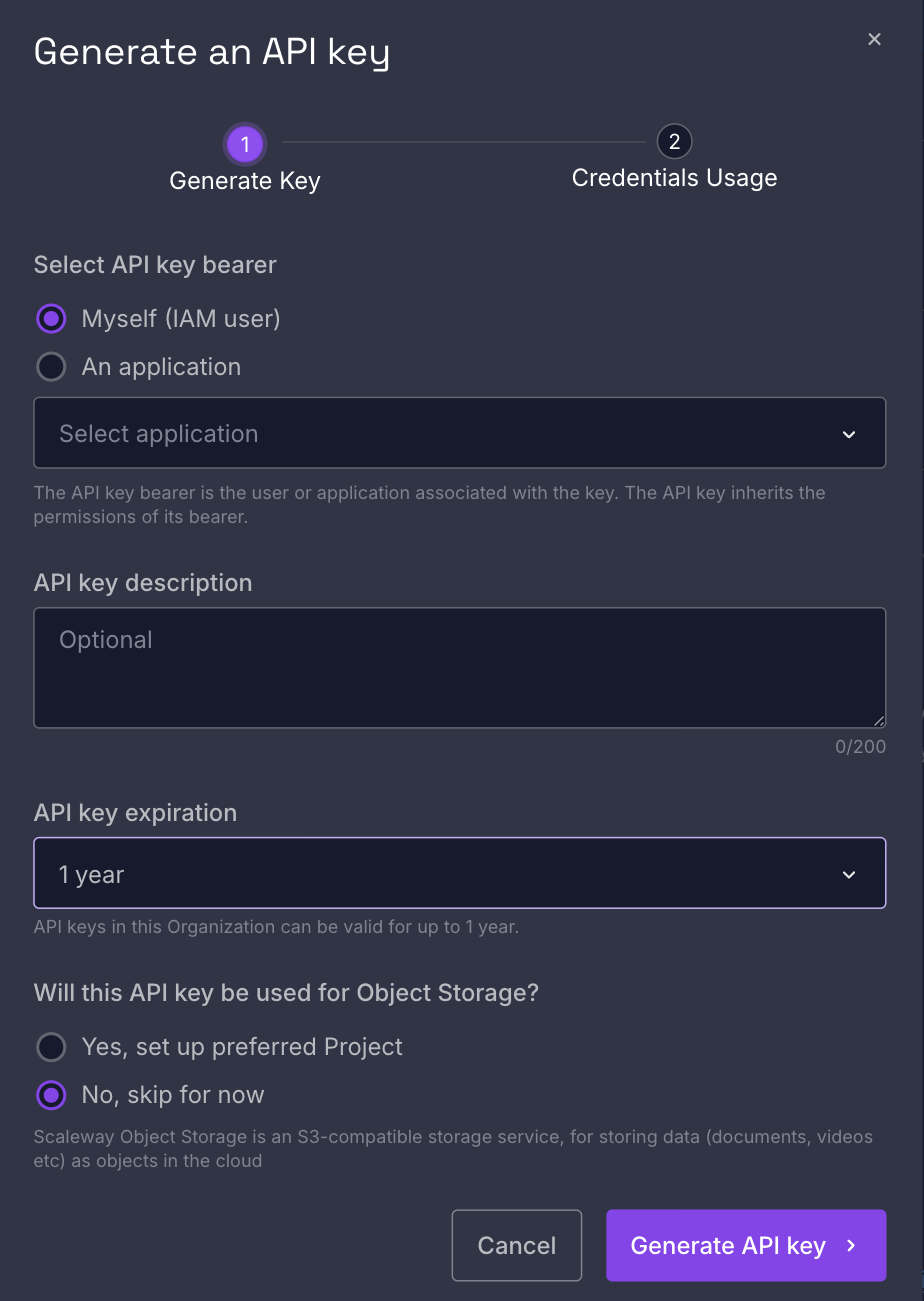
- In the Scaleway console, open IAM & API keys from the top-right menu, then the API keys tab.
- Click Generate API key, choose the bearer (yourself, or an IAM application that holds the
IAMReadOnlypermission), add a description (e.g.Probo Access Review), and generate it. - Copy the secret key (a UUID) and store it securely. It’s shown only once.
Step 2: Connect in the platform
Section titled “Step 2: Connect in the platform”- In the platform, go to Access Reviews > Sources > Add Source.
- Find Scaleway, click API Key, paste the secret key, enter your Organization ID (from Organization Settings), and click Connect.
the platform names the source after your Organization and pulls its IAM users into your campaigns.
Troubleshooting
Section titled “Troubleshooting”- Key rejected. Confirm you pasted the secret key (a UUID), not the access key (
SCW…) or the Organization ID. Only the secret key authenticates in theX-Auth-Tokenheader. - No users appear. The key’s bearer needs the
IAMReadOnlyorIAMUserReadOnlypermission, and the Organization ID must match the Organization you’re reviewing.